In many organisations, risks related to technology are handled as separate controls around projects, systems, or compliance checks. This provides oversight, but often leaves gaps between planning, development, and operations where risks emerge without clear ownership.
A more effective approach is to treat risk as part of everyday business and technology work. Decisions about capabilities, solutions, data, and services are made continuously, and each of these decisions carries both opportunity and risk. When these are considered together, organisations are better able to make balanced and informed choices.
The purpose is not to avoid all risk, but to make conscious decisions where opportunity, business impact, quality, business continuity, compliance, and ethical responsibility are considered together.
As the use of data, automation, and artificial intelligence increases, the nature of risk is also evolving. Decisions are no longer only made by people, but also by models and automated processes. This makes transparency, clear responsibility, and continuous oversight more important than before. At the same time, organisations increasingly consider sustainability as part of responsible technology use, ensuring that decisions support long-term environmental and societal outcomes.
Artificial intelligence and automation make risk more dynamic. AI agents, digital workers, automated workflows, and analytical models can influence decisions, user interactions, service behaviour, and operational outcomes at speed and scale. This increases the importance of clear ownership, traceability, monitoring, escalation paths, human oversight, and explainable outcomes. AI-supported work must be governed as part of the operating model, not treated as an isolated technology feature.
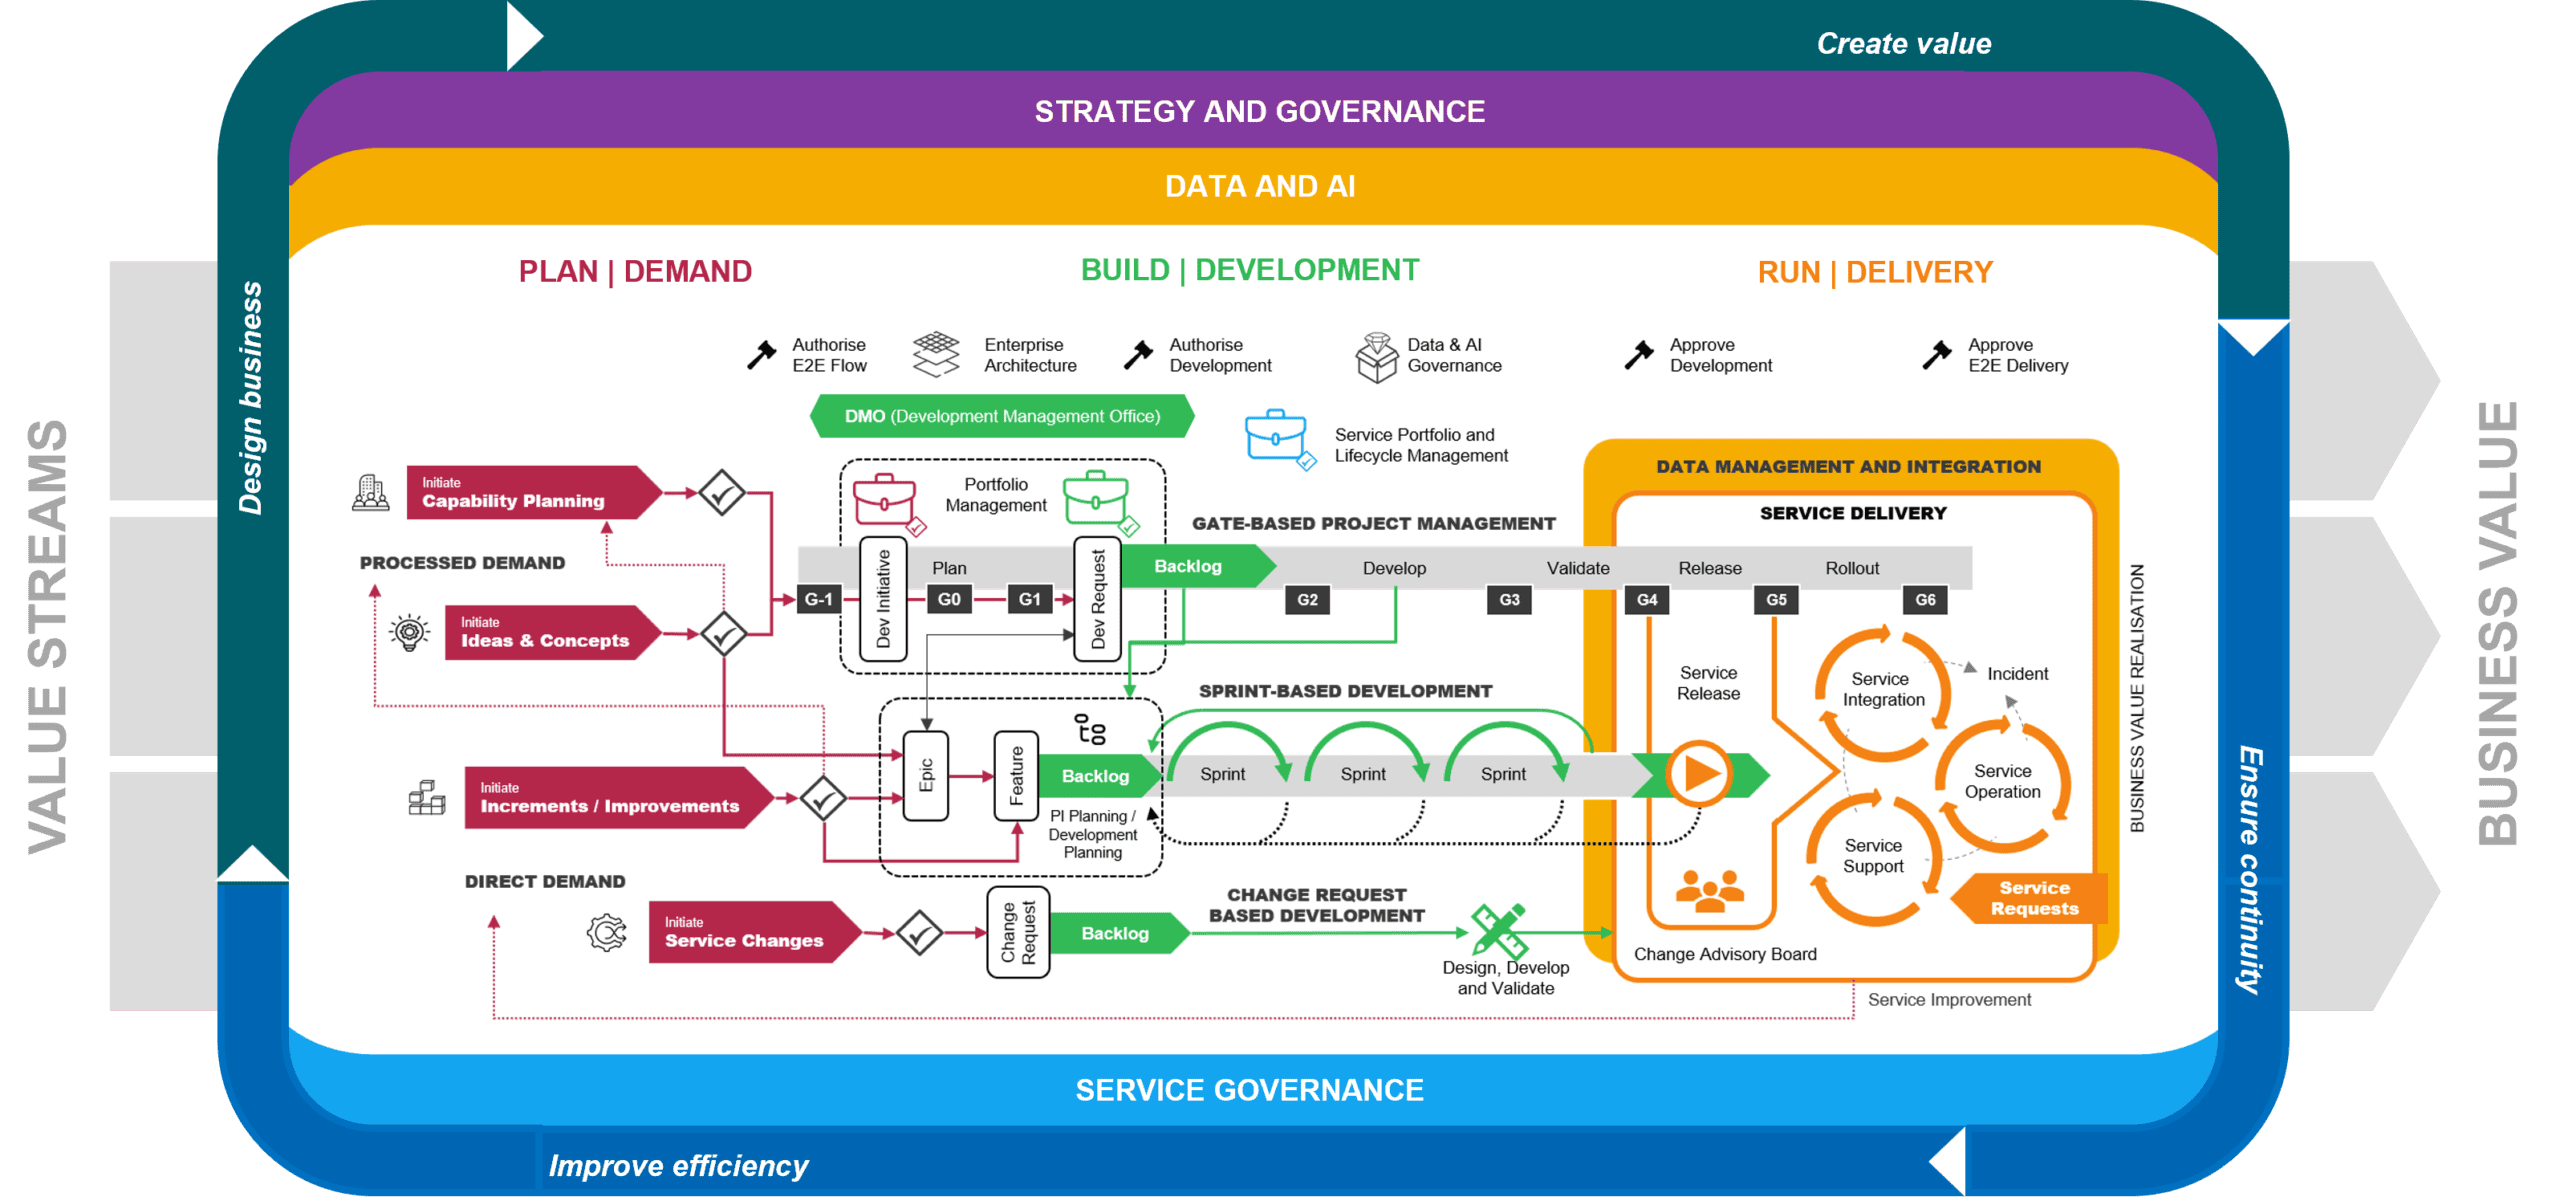
Business technology requires a constant balance between opportunity and risk. Risks do not appear in isolation. They emerge across planning, development, and operations, and often materialise when decisions are made without full visibility of their impact.
In planning, risks are linked to choosing the right direction and investments. In development, they are linked to execution, dependencies, and delivery quality. In operations, they are linked to continuity, performance, security, and user experience.
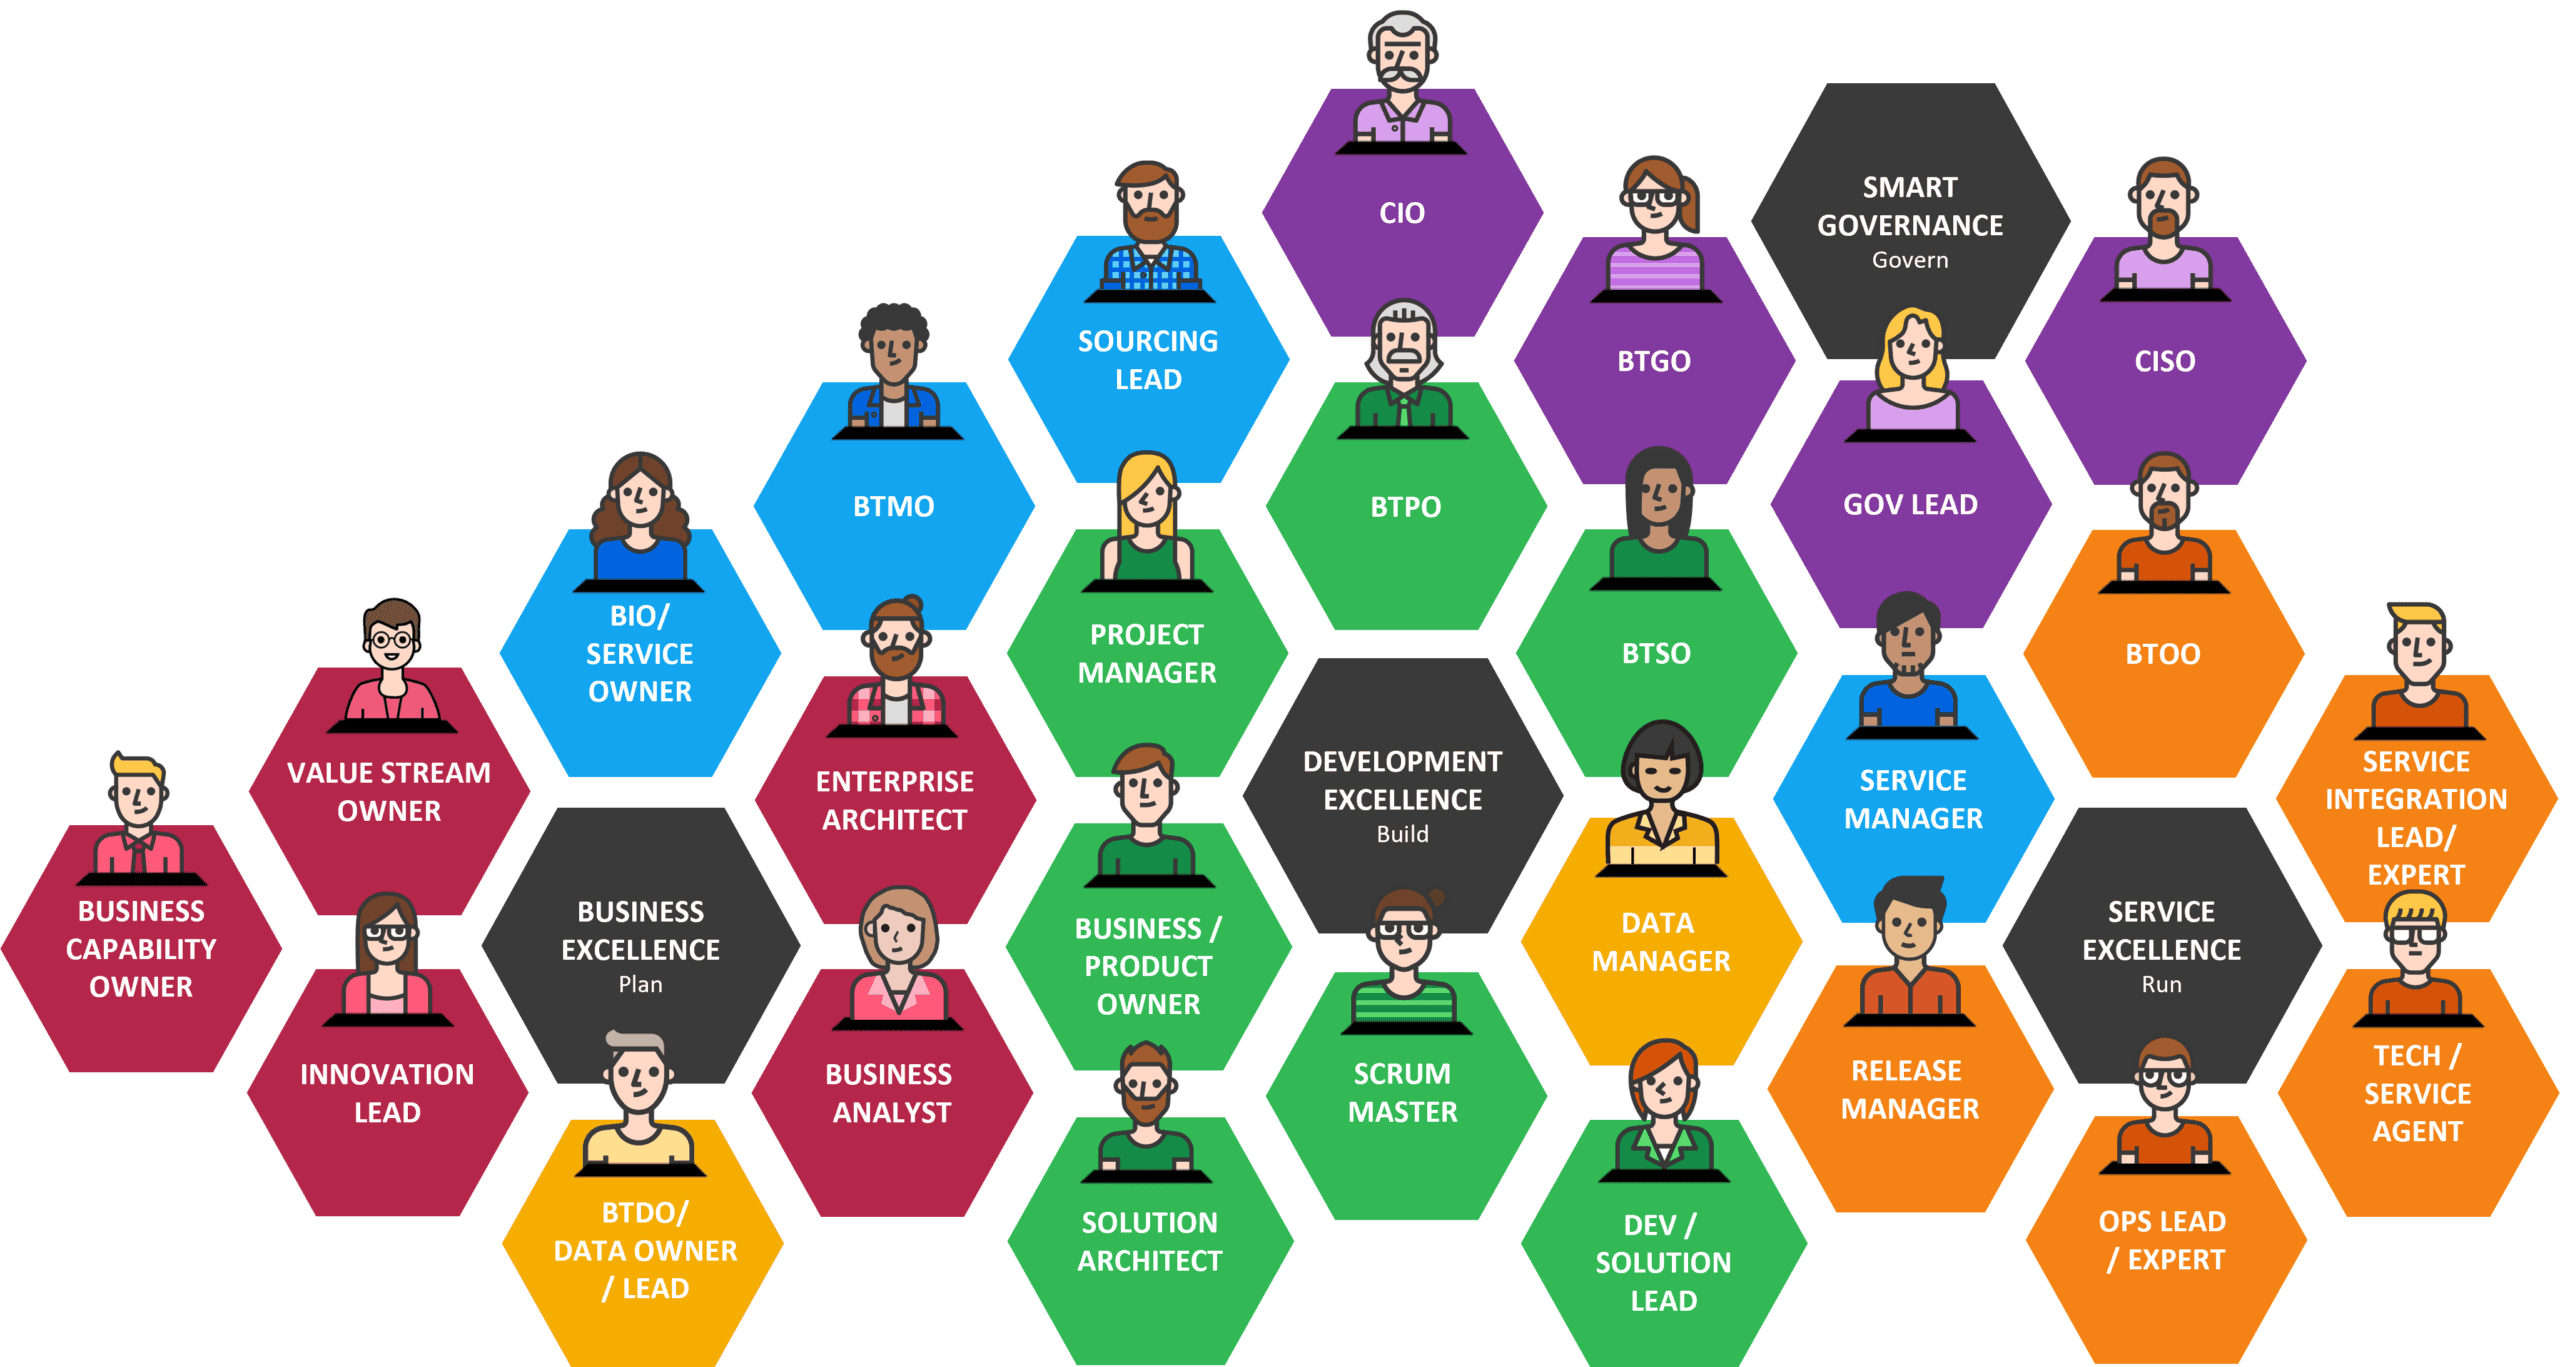
Managing risk is defined through roles. The accountable owner of the affected business outcome, service, product, data, solution or organisational area assesses the business impact of risk and decides what level of risk is acceptable within the agreed governance model. The Business Technology Governance Officer (BTGO) ensures that risk, quality, compliance, and ethics practices are embedded consistently into governance structures, decision points, and operating model practices across the organisation.
In practice, organisations respond to risks in different ways. Some risks are reduced through better controls or design choices. Others are accepted when the benefits outweigh the downside. In some cases, risks are avoided or transferred through sourcing and partnerships. The key is to make these choices consciously and with a clear understanding of their impact.
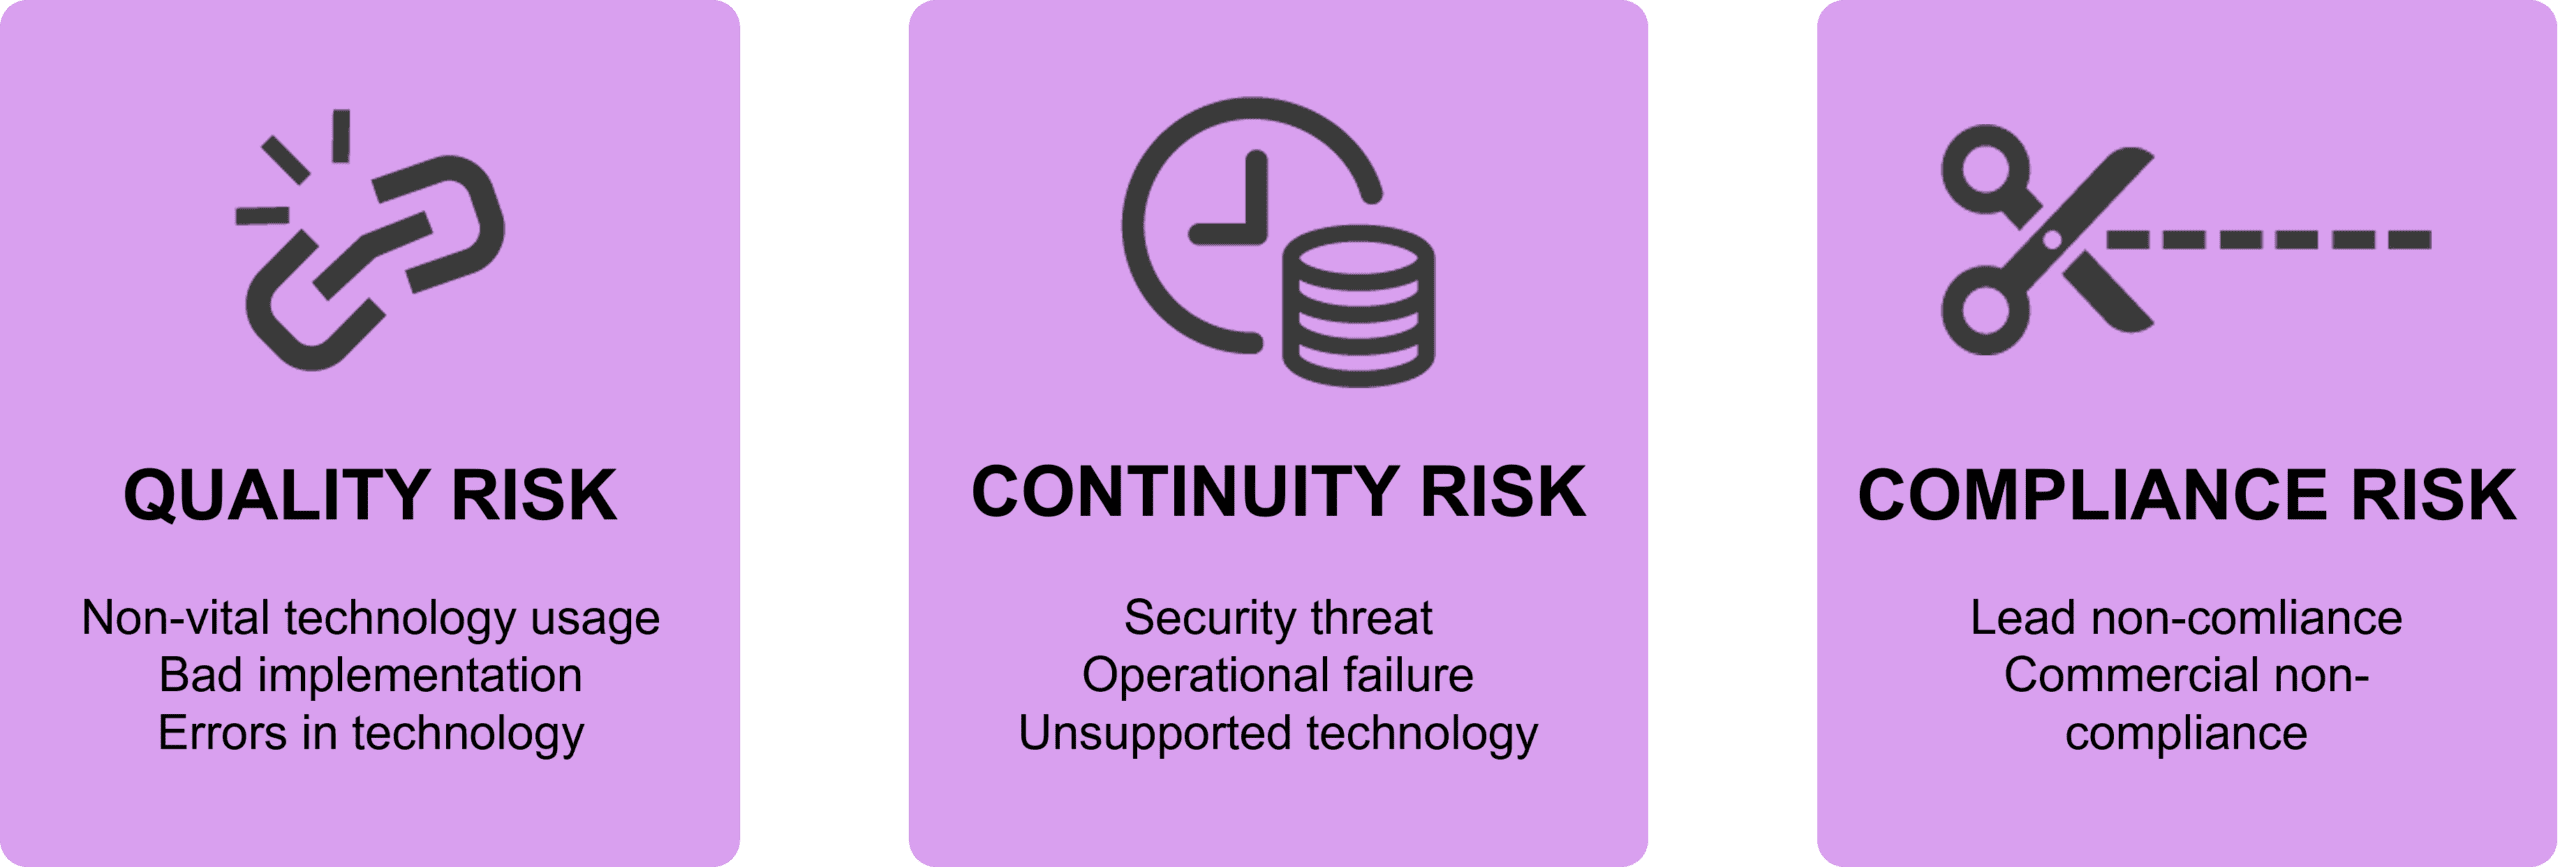
Business technology risk can arise across planning, development, services, sourcing, data, AI, finance and governance. Business technology risk is considered from several perspectives, including quality, business continuity and compliance.
Quality risks affect the organisation’s ability to deliver solutions and services that meet business needs.
Typical examples include:
These risks can affect business performance, customer outcomes and competitiveness.
Business continuity risks affect the organisation’s ability to keep critical services and operations available and recoverable.
Typical examples include:
These risks can affect revenue, customer trust and operational stability.
Compliance risks relate to adherence to laws, regulations, agreements and internal policies.
Typical examples include:
These risks can lead to financial, legal and reputational consequences.
Quality is about delivering what the business expects, in a reliable and consistent way. When quality is weak, it rarely appears as a single failure. More often it shows up as rework, delays, or outcomes that technically work but do not solve the right problem.
In practice, quality depends on how well people align early and how quickly they learn during delivery. When expectations are clarified together, assumptions are tested early, and feedback is used continuously, issues are identified sooner and are easier to correct.
Quality is therefore not a final checkpoint but an ongoing activity. Needs are shaped and validated early, solutions are developed in steps, and results are reviewed in real use. This creates a steady flow of feedback and reduces uncertainty.
Today, quality also depends on data and decisions. Reliable data, shared definitions, and clear processing logic are essential for reporting, analytics, and automated decision-making. If data is inconsistent or logic is unclear, outcomes can be wrong even when systems behave as expected.
Quality also has a sustainability dimension. Efficient use of resources, avoiding unnecessary processing, and designing solutions that last contribute both to cost efficiency and reduced environmental impact.
Clear ownership, simple change control, and regular feedback help maintain quality over time. The aim is not perfection, but dependable outcomes that support business needs.
Business continuity is about ensuring that critical business operations can continue, or recover quickly, when services, data flows, platforms, providers, automation, or operational processes are disrupted. It connects technology risk directly with business impact, because service interruptions can affect revenue, customer trust, regulatory obligations, and operational stability.
In business technology, continuity is not only a technical recovery topic. It depends on understanding which services are business-critical, how they depend on each other, how responsibilities are shared across internal teams and external providers, and how recovery is coordinated when disruptions occur. As organisations rely more on cloud platforms, automation, data, and AI-enabled operations, continuity must also cover automated workflows and digital workers, including how they are monitored, escalated, paused, or replaced by human action when needed.
Clear ownership, tested recovery practices, and continuous operational learning help maintain continuity over time. The aim is not to prevent every disruption, but to ensure that the organisation can respond quickly, recover in a controlled way, and protect the business outcomes that depend on technology.
Compliance ensures that business and technology activities follow laws, regulations, agreements, and internal policies. It is not a one-time effort, but a continuous responsibility that evolves as requirements change.
In practice, compliance requires organisations to regularly review how they operate and adjust their processes, services, and data practices when needed. Without this, gaps appear over time as regulations and expectations evolve.
Compliance has two main dimensions. Regulatory compliance focuses on laws and external requirements. Commercial compliance focuses on contracts, licences, and agreed terms. Both shape how services are delivered and how technology is used.
Modern compliance also extends to data, automation, and AI-enabled decisions. Organisations need to ensure that data is used appropriately and that decisions can be traced and explained when required. This becomes more important when services are delivered through ecosystems where responsibilities, data usage, and operational decisions may span several internal and external parties.
Clear roles, structured processes, and well-maintained documentation make compliance manageable. They help ensure that obligations are understood, applied consistently, and can be demonstrated when needed.
Ethics ensures that technology is used in a responsible and transparent way.
Ethical questions arise when decisions affect people, customers, or business outcomes. As organisations rely more on data and automation, these decisions are increasingly influenced by models and algorithms rather than direct human judgement.
This makes it important to consider ethical aspects early. Questions of fairness, transparency, potential impact, and sustainability should be part of how solutions are designed and implemented, not addressed afterwards.
Ethical behaviour is supported by clear guidelines, defined responsibilities, and awareness across the organisation. People need to understand not only what is allowed, but also what is appropriate in different situations.
At the same time, decisions made by systems should remain understandable. When outcomes can be explained and responsibility is clear, trust is easier to maintain. Responsibility cannot disappear into automation, AI agents, or external platforms.
By treating ethics as part of everyday work, organisations can ensure that technology supports both business objectives and responsible, sustainable use.